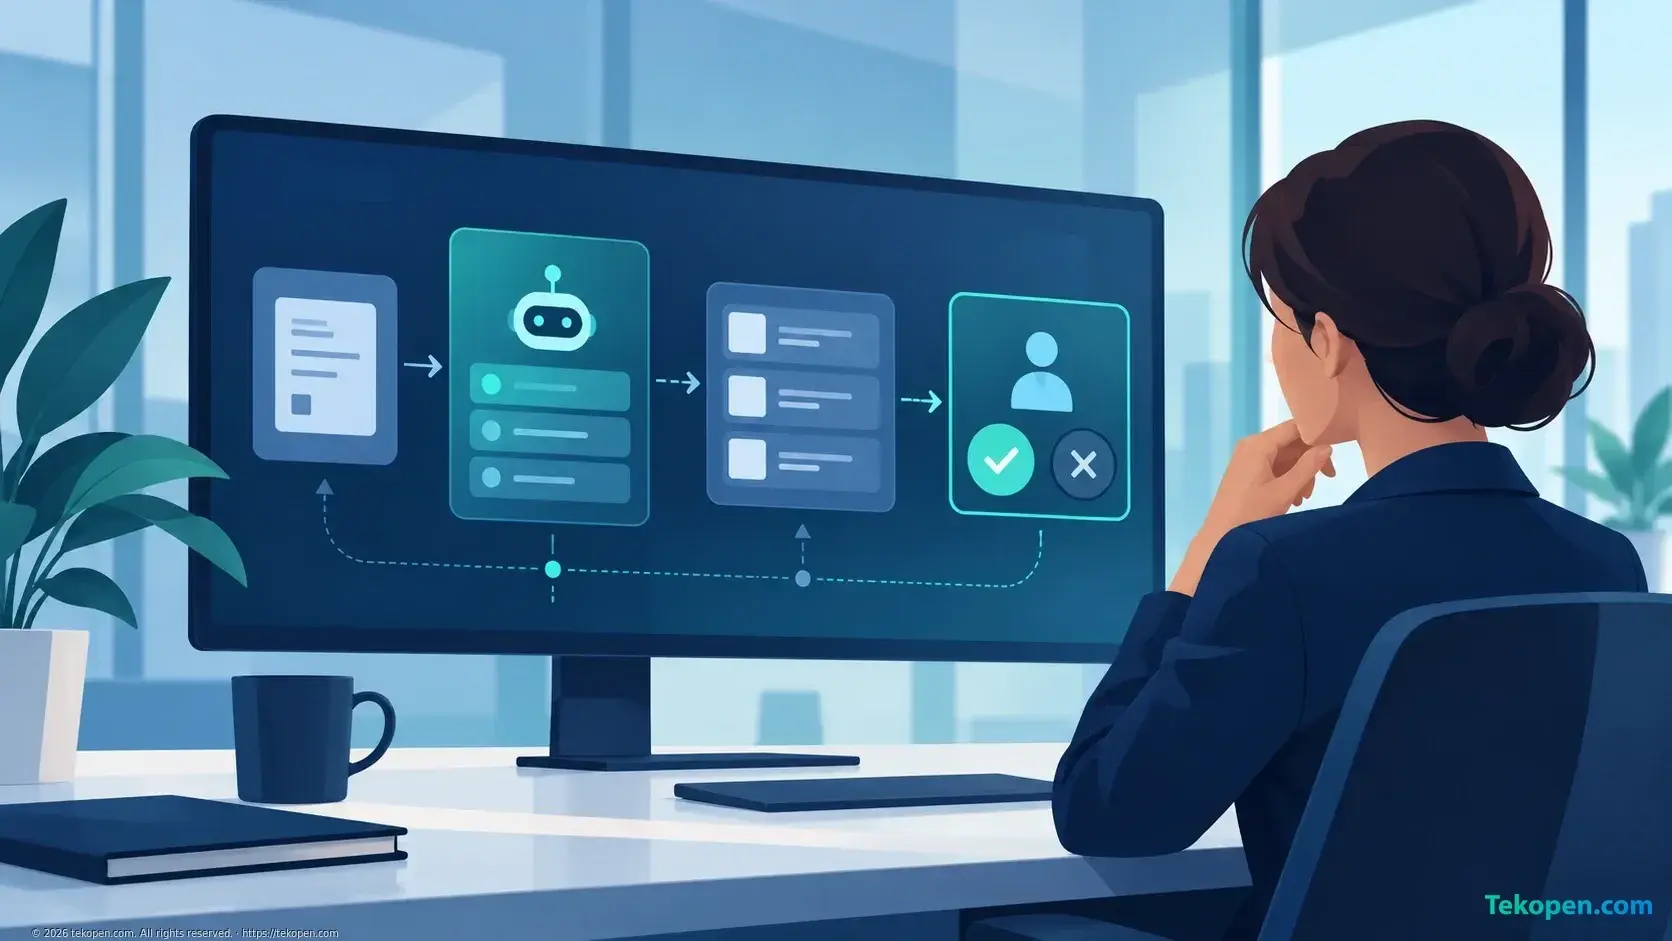
AI agents should be allowed to handle low-risk steps that have a clear scope and are easy to verify on their own; actions that alter important data, incur costs, or create commitments to external parties need appropriate approval mechanisms. These boundaries should be defined before execution, rather than leaving AI to infer them as it works.
In its guide to building with the GPT-6 model family published on October 2, 2026, OpenAI recommends that deployment teams clearly state which decisions the model can make on its own and when it must ask the user. What matters here is not just the model’s capabilities, but how permissions to act are structured when AI takes part in multistep work.
From Answering Questions to Performing Tasks
With a conversational assistant, users typically receive a draft and then decide whether to use it. When AI is connected to tools, it can find documents, run tests, or coordinate multiple steps in a workflow. At that point, checking the final answer is not enough: businesses also need to control the actions that took place beforehand.
OpenAI’s guidance suggests replacing blanket rules such as “always ask first” with specific boundaries. For example, the model can choose how to organize a summary on its own, but needs to ask before changing the project’s scope. For programming work, the instructions may allow local tests using disposable data, without access to the production environment.
This is a deployment recommendation, not a guarantee that the model will always comply. Access permissions and approval mechanisms still need to be designed at the application level.
Divide Action Permissions into Three Categories
One practical approach is to divide tasks into three categories: allowed autonomously, requiring approval, and prohibited. The table below is a reference framework for businesses, not an official OpenAI classification.
Action category | Examples | Appropriate controls |
|---|---|---|
Allowed autonomously | Summarizing documents with authorized access, creating drafts, testing in an isolated environment | Limit the scope and save results for review |
Requires approval | Sending external emails, updating customer records, deploying changes | Show the content and impact before confirmation |
Prohibited | Accessing out-of-scope data, deleting important data, changing its own permissions | Block through system permissions, not just instructions |
The same operation can fall into different categories depending on the circumstances. Editing content on a draft website is different from editing a page currently serving customers. Reading an ordinary internal document is also different from reading sensitive personnel records.
Actions should therefore be assessed based on the data used, who or what is affected, and whether they can be reversed, rather than solely on the tool’s name.
Clear Prompts Are No Substitute for Access Controls
An instruction such as “do not send emails without approval” is necessary, but does not constitute a complete layer of control. If the tool still allows direct sending, the system remains dependent on the model understanding and following the instruction in every situation.
A more reliable approach is to separate drafting from execution. AI prepares the recipients, content, and attachments; an authorized person reviews them; the application only allows sending after confirmation.
Similarly, a coding agent can work in a test environment without being given production credentials. Restricting permissions from the outset helps reduce the consequences if the model misunderstands a request or mishandles input documents.
For teams just starting deployment, how to get started using AI to support work remains a suitable foundation: choose a small task, define a clear output, and check it before expanding.
Approval Checkpoints Must Help People Make Decisions
A notification with only an “Agree” button can easily turn approval into a formality. A useful checkpoint needs to tell the reviewer:
What action AI is about to take and who or what it will affect.
What data or evidence led to the proposal.
What content will be changed, sent, or recorded in the system.
Whether the action can be canceled or reversed.
For example, before updating a CRM, the system should display the current and proposed values. Before sending a quote, the approver needs to see the recipient, price, and applicable terms, rather than simply reading “email prepared.”
The team also needs to identify who is responsible for approval and how to proceed when that person is absent. A Trello task management board can help track tasks awaiting confirmation, although it does not replace the mechanism that blocks actions within the application.
Define “Done” Before Assigning Work
OpenAI also recommends clarifying completion criteria: not just making changes, but also running them, checking the results, and handling errors within the permitted scope.
For businesses, a task should not be marked done simply because AI has generated content. For example, “prepare a report” may need to include cross-checking sources, identifying missing data, and handing it over to the person responsible. “Fix a software bug” requires test results, not just new code.
The statuses “processed by AI,” “awaiting approval,” and “completed” should be clearly distinguished. If a customer service workflow includes time commitments, how to create a clear SLA helps define responsibilities and measurement methods, but an SLA itself does not guarantee the quality of AI output.
Conclusion
A notable point in OpenAI’s new guidance is that autonomy needs to be designed alongside the task, not added after tools have been connected. Businesses should start with a narrow scope, separate preparation from execution, and also test situations in which AI must stop. A useful agent does not just know how to keep going; it also needs to know when to hand a decision over to a person.
Frequently Asked Questions
How does an AI agent differ from an AI assistant that only answers questions?
AI agents are typically designed to coordinate multiple steps and use tools to achieve a goal. The key difference is their ability to act: if granted permission, they can affect systems rather than simply provide content for users to read.
Should AI be required to ask for permission before every operation?
Not necessarily. Asking for permission for every small step can cause overload and lead approvers to confirm out of habit. Approval checkpoints should be prioritized for actions with significant consequences, while low-risk preparatory steps are allowed to run within a limited scope.
How can you test whether AI stops at the right time to ask for permission?
Create test scenarios such as out-of-scope requests, missing recipients, price changes, or the use of data without authorized access. Check both whether the agent recognizes the boundaries and whether the application actually blocks the action without confirmation.
Which tasks should businesses try AI agents on first?
You can start with preparing drafts or compiling documents from an approved data source. Prioritize tasks whose results are easy to cross-check, that do not independently create external commitments, and that do not require permission to modify important data.